
At home, setting up a network can feel simple. Connect the router, choose a Wi-Fi name, enter the password, and start adding devices. That convenience is useful in a household where a few people generally trust one another and the network mostly needs to reach the internet. A business has a different job to do.
An office network may connect employee laptops, company servers, printers, cameras, door systems, phones, guest devices, and equipment that cannot be updated as often as a normal computer. Those devices do not all need to communicate with one another. Treating them as if they do can turn one small problem into a much larger one.
One building does not mean one open room
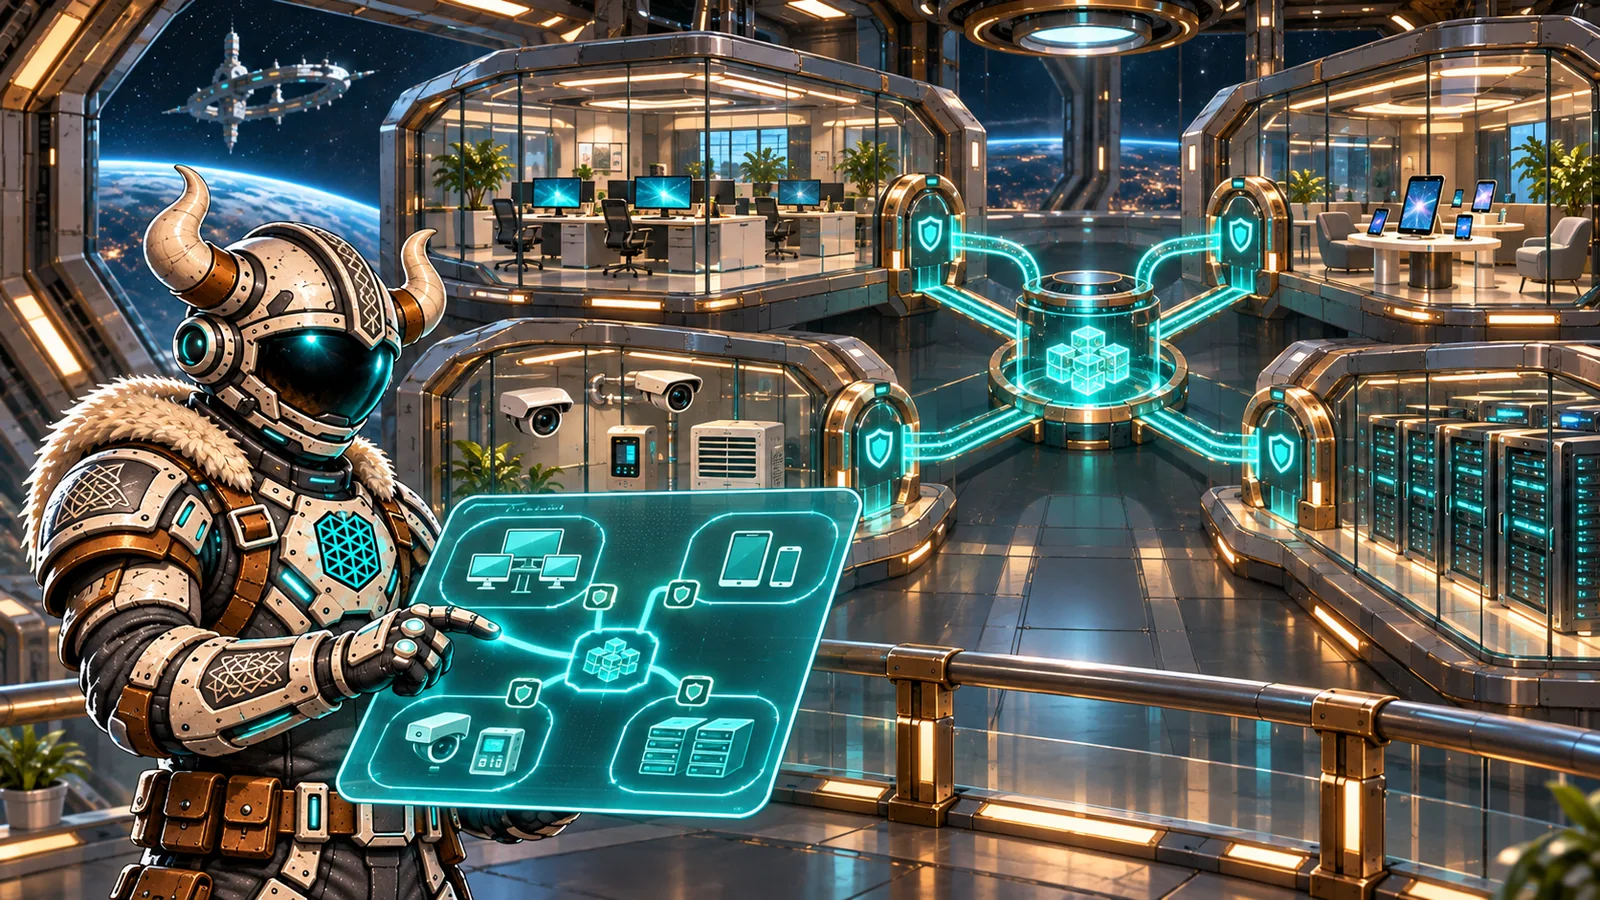
Think of a business network like the building it supports. Visitors may be welcome in the lobby, employees can enter work areas, and a smaller group may have access to finance records or the server room. The building still functions as one workplace, but doors help people reach the areas they need without making every room public.
Network segmentation applies the same idea digitally. Devices are grouped according to what they do, what they need to reach, and how much protection they require. Rules between those groups control the traffic that should pass and stop traffic that has no business reason to cross.
Source: NIST security segmentation guidance for small organizations
What might be separated?
The right groups follow the work of the organization. A small professional office and a manufacturer will not need the same design. The goal is not to create a complicated diagram for its own sake. It is to give each device the access needed for its job and avoid unnecessary paths to everything else.
- Employee devices may need business applications, printers, and selected internal services.
- Guest devices usually need the internet, not access to company computers or shared files.
- Cameras, door controllers, televisions, and other building devices can be placed apart from normal employee work.
- Servers and administrative systems can receive tighter rules than ordinary workstations.
- Specialized or older equipment can be limited to the few systems it actually needs.
A virtual local area network, often called a VLAN, is one common way to create these logical groups on shared switching equipment. A firewall or another policy-enforcement point then controls communication between them. The names of the technologies matter less to most employees than the outcome: a guest can join Wi-Fi without being placed beside the accounting computer.
Source: NIST definition of a virtual local area network
Segmentation limits the reach of a problem
Segmentation does not make a device safe by itself, and it does not replace updates, strong identity controls, backups, or monitoring. It helps reduce unnecessary trust. If a camera, guest phone, or employee laptop develops a problem, the network rules can limit which other systems are directly reachable from that starting point.
CISA describes proper segmentation as a way to make lateral movement more difficult and contain the effect of an intrusion. In plain language, an intruder who gets into one room should not automatically receive keys to the rest of the building.
Source: CISA guidance on segregating networks and functions
Why not use the same setup as home?
A home router is designed to make a common household setup quick. Business networks must account for more people, more types of devices, valuable company information, remote access, multiple locations, and the need to understand what happened when something fails. They also need a deliberate process for adding and removing access as employees, vendors, and equipment change.
Business equipment can still make routine setup easier, but easy onboarding should happen inside a planned design. Plugging in a new switch or access point without understanding its configuration can extend the wrong network, bypass an intended control, or create a second set of settings no one is watching. Convenience is useful when it follows the plan.
Good segmentation should support the working day
A network can be divided badly. Rules that are too broad fail to create meaningful separation. Rules that are too narrow can interrupt printing, calling, building access, or a specialized application. Before making changes, document the devices, the services they use, and the people responsible for them. Then test the required paths and the paths that should be blocked.
- Inventory the important devices and identify who owns each system.
- Group devices by business purpose and communication needs, not just by where they sit.
- Define the traffic that must cross between groups and who can approve a change.
- Test real work such as printing, calling, remote support, and vendor maintenance.
- Monitor the result and review it when the business adds people, locations, or equipment.
The result should not feel like extra work every time someone opens a laptop. Most people may never see the boundaries at all. They notice that the connection works, guests have an appropriate way online, and the systems behind the business are not all sharing one open room.
RIKR can help map what is connected, design practical network zones, and manage the switching, wireless, and firewall policies that keep those zones useful. The objective is not complexity. It is a network built around the way your business actually works.
Related: what Wi-Fi density means for a business
Written by Joshua Price
Back to the blog